A cyber insurance security questionnaire is easier to complete when your answers are backed by current records. Instead of relying on memory or assuming that a security product covers every system, gather evidence that shows what is configured, which users and devices are included, and where exceptions exist.
There is no single evidence pack that fits every business or policy. An insurer’s application and follow-up questions determine what is relevant. Use the checklist below to organize your records, then compare each item with the actual questionnaire before submitting answers.
Build an evidence folder around the questionnaire
Start with the application itself. Read each question closely and note the systems, accounts, locations, or types of data it asks about. A question about multifactor authentication, for example, may have a different scope from one about remote access or administrator accounts.
Create a secure folder for the records you collect. For each control, note:
- What it covers: The relevant systems, users, devices, or data.
- Who owns the evidence: The person or provider who can verify the information.
- When it was checked: The date of the report, review, or test.
- Known exceptions: Any systems, users, or situations that are not covered.
- Where the record came from: Such as an administrative console, IT provider, or internal policy.
Keep the folder access-controlled. Security reports can reveal details about your systems, and insurers may have instructions for how to submit supporting material. The NIST Cybersecurity Framework 2.0 Small Business Quick-Start Guide can also help organize a general review of your cybersecurity practices.
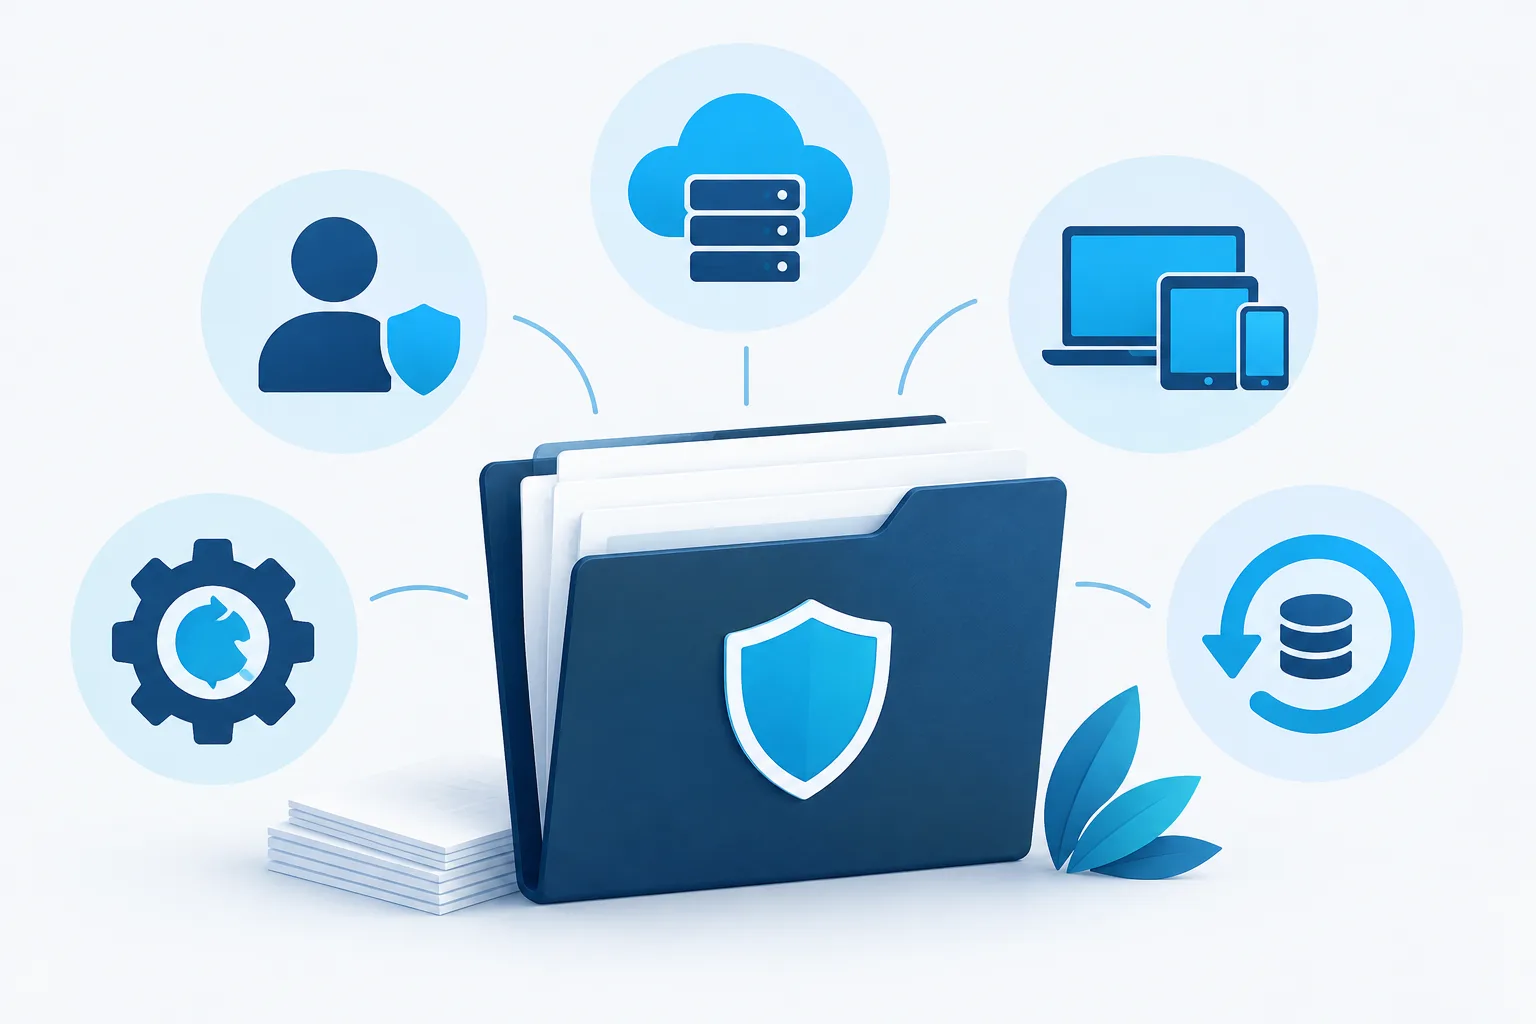
Cyber insurance evidence checklist
MFA and account access
For MFA evidence, collect configuration views or reports that show whether multifactor authentication is enforced, not merely available. Check the scope requested in the application, which may include email, remote access, administrator accounts, and cloud services.
Compare the report with your current user and system lists. Record any accounts or services that are excluded, and confirm whether the exception is approved or still needs attention. A written policy can explain your intended approach, but it does not by itself show that a setting is active across the requested scope.
Backups and recovery testing
Gather backup configuration details for the critical systems and data named in the questionnaire. Useful records may show what is backed up, the schedule, retention settings, and the latest job results. Check that the records cover the systems you intend to include in your answer.
Pair backup records with a dated restore-test record. Note what was restored, who performed the test, the result, and any follow-up work. A successful backup job does not establish that the business has tested recovery. If a restore test is not documented, record that as a gap rather than implying the process has been proven.
If your organization has not reviewed its recovery procedures recently, the article on business continuity planning offers related considerations for preparing to continue operations through disruption.
Endpoint protection and device coverage
Collect a current device inventory alongside an endpoint protection or antivirus console report. The records should help you compare the devices in scope with the devices reporting active protection. Note systems that are missing, inactive, or managed differently, and ask the control owner to verify any unclear status.
A product name or purchase record alone does not show that protection is installed and operating on the relevant devices. Keep evidence that reflects the current configuration and coverage, while following your insurer’s directions about what documentation to provide.
Software updates and patching
Gather patch or update reports for the systems named in the application. Change records or maintenance notes can help explain when updates were applied, what systems were covered, and how exceptions or delayed updates were handled.
If reports show outstanding updates, confirm whether they apply to systems within the questionnaire’s scope and record the status accurately. Avoid presenting a general update policy as proof that every system is current.
Incident response, continuity, and staff preparation
Have current copies of your incident response and business continuity plans available if the application asks about them. Check whether the documents identify responsibilities, communication steps, and recovery priorities relevant to your business. If the plan has been reviewed or exercised, keep a record of what was reviewed, when, and any follow-up actions.
If the questionnaire asks about employee security awareness, gather the materials used and records of completed training or acknowledgments, where available. Make sure the evidence reflects your actual process rather than an intended future program.
MSPs, cloud providers, and other vendors
Some controls may be operated by an IT provider, cloud provider, or other vendor. Ask who manages each control and what records they can supply. Depending on the question, useful documentation might include a description of responsibilities, access arrangements, configuration evidence, or service reports.
Make sure you understand which systems and accounts the provider’s evidence covers. A provider-managed control does not automatically establish coverage for every part of your business. If responsibility is shared, document which party handles each part and note any area that remains unconfirmed.
Check accuracy before submitting
Review each answer against both the questionnaire’s wording and your evidence. Distinguish between a written policy, a control that is configured, coverage across the requested systems or people, and evidence that the control has been tested or reviewed. Those are related, but they are not interchangeable.
Ask the relevant control owner or IT provider to verify technical answers, especially when they involve MFA scope, backup status, endpoint coverage, or patching. Record partial coverage and unknowns clearly. If an answer depends on how the insurer interprets a question, ask the insurer or your insurance professional for clarification rather than guessing.
A sample insurer application can help you see how specific questions may be phrased, but it should not be treated as a universal checklist. For example, the Great American cyber insurance application is one example; the questions and evidence requested for your own application may differ.
For broader preparation, Zevonix’s guide to small-business cybersecurity practices can help you review the controls behind your documentation. Zevonix provides managed IT support, cybersecurity, and strategic IT planning for businesses in Palm Coast, Flagler Beach, Bunnell, and surrounding Flagler County.
Frequently asked questions
How can a business prove MFA is enforced?
Use current configuration views or reports, then compare them with the specific accounts and systems named in the questionnaire. Document exclusions instead of relying only on a policy or a statement that MFA is available.
What records show that critical systems and data are backed up?
Collect backup configuration details and job records that identify the systems or data covered. Add a dated restore-test record showing what was restored and the outcome.
What should a backup restore-test record include?
Record the test date, what was restored, who performed the test, the result, and any follow-up needed. Keep the entry tied to the relevant system or data set.
What if a control is managed by an IT provider?
Ask the provider for evidence that matches the questionnaire’s scope, and document who is responsible for each part of the control. Note any coverage you cannot confirm.
Before you submit, make sure each answer matches the application and the evidence you can support. If you need help reviewing technical records or identifying coverage gaps, contact Zevonix to discuss your business’s IT needs.